Skip to content
New York · Custom Business Software

Custom software for New York teams.

Softglimmer develops custom business software for New York teams whose workflows no longer fit disconnected tools or spreadsheets. We compare configuration, integration and a focused custom build, then agree the users, records and acceptance needs. Our Ranchi studio collaborates remotely through documented decisions and demonstrations, with migration, deployment, ownership and ongoing responsibilities defined before the first release.

Explore New York
A useful business application with an operating plan.
  1. 01

    Map the workflow

    Name the roles, records, decisions and recurring exceptions.

  2. 02

    Implement the right scope

    Connect the agreed interface, business rules and approved systems.

  3. 03

    Prepare operation

    Define acceptance, switching, ownership and support.

An example journey, shaped around your requirements.

Solve the operational gap before choosing a custom build.

The custom-software service is for business workflows whose roles, data or decisions do not fit the current collection of tools. The first conversation compares configuring an existing product, joining approved systems and building an application. A useful first release should prove an essential workflow instead of accumulating dashboards without clear users.

The scope can include a role-based interface, business records and permission rules, approved API/data connections and the application logic linking them. We also review any migration, deployment and operating responsibilities. Existing-system access and provider limitations affect what can be delivered and estimated.

The shared-request illustration below explores one set of role relationships. Other internal or customer-facing business workflows can be reviewed against their own records and decisions. This page does not promise every kind of software or a predetermined technology stack.
Configure, connect, or develop the required application.

The choice follows the process and operating requirements, not an assumption that a new codebase is always the answer.

01

Configure a product that fits

Compare a suitable existing product with the actual users, records and rules. Retaining a practical tool may reduce implementation and operating effort.

Discuss before build: Explain the fit gap before replacing it.

02

Connect the approved systems

Review documented APIs, exports or permitted connection methods and identify which system owns each record. Integration can solve a gap without rebuilding every application.

Discuss before build: Feasibility depends on access and provider constraints.

03

Build a focused business application

Develop the agreed interface and business rules when a meaningful process or integration gap justifies a custom application. Stage later modules behind a useful first release.

Discuss before build: Named acceptance cases and an operating plan.

Specify the application, data and operating outputs.

The proposal names the selected workflow and its dependencies. Migration, new backend work and integrations are included explicitly when required.

01

Workflow and first-release brief

Map users, recurring work, exceptions and the existing tools. Agree what the first release must accomplish and what can wait.

Documented requirements and acceptance priorities.
02

Record and permission model

Define business records, relationships, authoritative data sources and the actions each role can perform.

Clear access and ownership decisions.
03

Role-based working interface

Design forms, views and actions around the scoped tasks, including errors and empty states.

Screens and states users can assess.
04

Application and approved integrations

Implement the agreed rules and supported data/API connections, with maintainability and provider limits accounted for.

Demonstrable application milestones.
05

Migration and acceptance evidence

Plan data transfer, reconcile representative records and check the complete workflows with the people approving them.

Acceptance conditions before switching.
06

Deployment and operating handover

Document deployment, backups, support owners and the procedure for later changes. Specify source, data, accounts and external dependencies in the agreement.

An operating plan rather than an unexplained code delivery.

Take the agreed workflow through review, release and operation.

For an estimate, share the current process, intended roles, representative records, existing applications and available integration methods. Identify migration needs, critical acceptance cases, switching constraints and who will own the system afterward. Ranchi-based remote delivery uses agreed meeting windows, written decisions and demonstrations; we schedule the required New York review participants rather than assume continuous shared office hours.

  1. 01

    Discover and compare

    Review the business gap and configuration/integration alternatives. Define the first-release dependencies and uncertainties.

    A scoped brief and implementation estimate.
  2. 02

    Design and develop

    Review relationships, permissions and task screens, then implement the agreed business rules and connections in visible milestones.

    Demonstrations against the named workflow.
  3. 03

    Accept and deploy

    Reconcile scoped migration records and test roles, exceptions and integrations. Agree the switch and recovery responsibilities before release.

    A deployment and acceptance plan.
  4. 04

    Handover and maintain

    Explain the deployment, data and administrative responsibilities. Confirm what the business owns and what depends on third parties; define support and later changes separately.

    Documentation and named operating owners.

Commission software around the shared request.

We can scope the request model, role-aware interface, server checks and operating handover for this workflow. The existing records, users and source systems determine whether the first implementation belongs in a current application or a new bounded tool. Payment processing, connected accounts and automatic customer communications are separately identified requirements rather than assumed features.

Share a sanitised request and the change rule through the project enquiry. We review the current process before proposing a written estimate, implementation stages and acceptance examples. A commissioned build should demonstrate the permitted and refused actions, current-state presentation and correction route. Your operating owner supplies the authority decisions; the technical work makes those rules explicit and testable.

A hypothetical working example

An organiser requests a change that also affects the recipient and payer.

Consider a hypothetical New York organisation arranging a service for a colleague. An organiser supplies the request, the colleague receives the service and another person handles the payment reference. The organiser later asks to change the date. Staff need to know whether that organiser can approve the change, whether another owner must review it and which people need the updated information. A first software phase can handle those relationships and the current instruction. It should not assume a payment reference grants authority over every service decision.

Roles belong to the request

Record the organiser, recipient and payer as explicit relationships to this request. One person may have several roles, but matching an email address should not erase the distinctions. Review an example with a shared address or a role that changes. Keep the source of each assignment visible so staff can resolve uncertainty instead of guessing from the contact list.

The proposed change is not yet the instruction

Show the existing agreed date alongside the new request until the authorised review is complete. Identify the person proposing the change and the owner who may accept it. A correction to a contact detail can use a different rule from a change to the service. The brief should define those differences before one broad edit permission is applied.

Keep the organiser, recipient and payer roles explicit when several people share one request.
  1. 01

    Identify the people and roles

    Keep each contribution linked to the request.

  2. 02

    Review the requested change

    Check who may propose and approve this decision.

  3. 03

    Confirm the current instruction

    Show what is agreed and what remains pending.

Illustrative project planning sequence.

Define who may make each decision, then connect the system.

01

Map the people without inventing authority

Separate contact information, request roles and decision rights. Ask your owners which facts the organiser can supply and which require confirmation from someone else. Include a missing role and a request made on another person’s behalf. Payment-related fields can identify the relevant record without turning the system into an unscoped payment-processing project.

02

Enforce the agreed permission rule

OWASP recommends checking permissions on every request. If a role may approve one type of change, that decision needs a server-side rule as well as a clear interface. Review an unauthorised attempt and a user whose relationship has changed. The implementation must not infer universal authority from the payer label or a visible approval button.

03

Keep the current state and proposal distinct

Define the agreed service instruction, a pending change and the reviewed outcome. Identify which earlier facts remain useful for staff and how a mistaken acceptance is corrected. The request history should explain the change without presenting every draft as a confirmed service. Confirmation and customer communication are separately scoped responsibilities.

04

Share the information each role needs

Decide what the recipient, organiser and payer actually need to receive or view. Avoid copying the full request to everyone by default. Scope delivery channels and approval separately, including a failed delivery and an outdated address. A software review can end with the accepted instruction and internal task; it does not need to send a message.

A shared-request model with accountable change decisions.

01

Role and decision map

People, request relationships and permissions for the selected service task. Examples show one person with several roles, a shared address and a relationship that changes. The map identifies the business owner for unresolved authority questions and the source of each supplied fact.

02

Change review workflow

A prototype or scoped implementation plan separating the current instruction from the proposed change. It includes an authorised acceptance, a refusal and a correction example. The notes identify backend checks, retained context and which steps require a named human owner.

03

Handover and integration boundaries

Acceptance cases for role assignment, permission checks and current-state presentation. The handover names any systems or communication channels proposed for a later phase and their prerequisites. It records what the first release actually does, without claiming payment processing or universal approval automation.

Review one shared request with all three roles visible.

Bring a sanitised request and explain who organised it, who receives the service and which person owns the payment reference. Choose one meaningful change, such as a new date, and write down the approval rule. Include a request where the payer and organiser are the same person and another where they differ. The software should express the rule consistently in both examples.

Let a member of the operating team review the proposed change. Ask which instruction remains current, who may accept the proposal and what should happen if that role is missing or uncertain. Then correct a deliberately mistaken assignment. Inspect what each authorised role can see, rather than judging only the administrator view. Those examples expose the work needed in the data model, interface and server permissions.

Remote New York reviews can focus on this bounded workflow with our Ranchi studio. The owner receives a written account of the approved states and outstanding decisions before integrations are proposed. A service request that staff can explain clearly provides a practical starting point for custom software; adding more contact fields alone will not settle responsibility or approval.

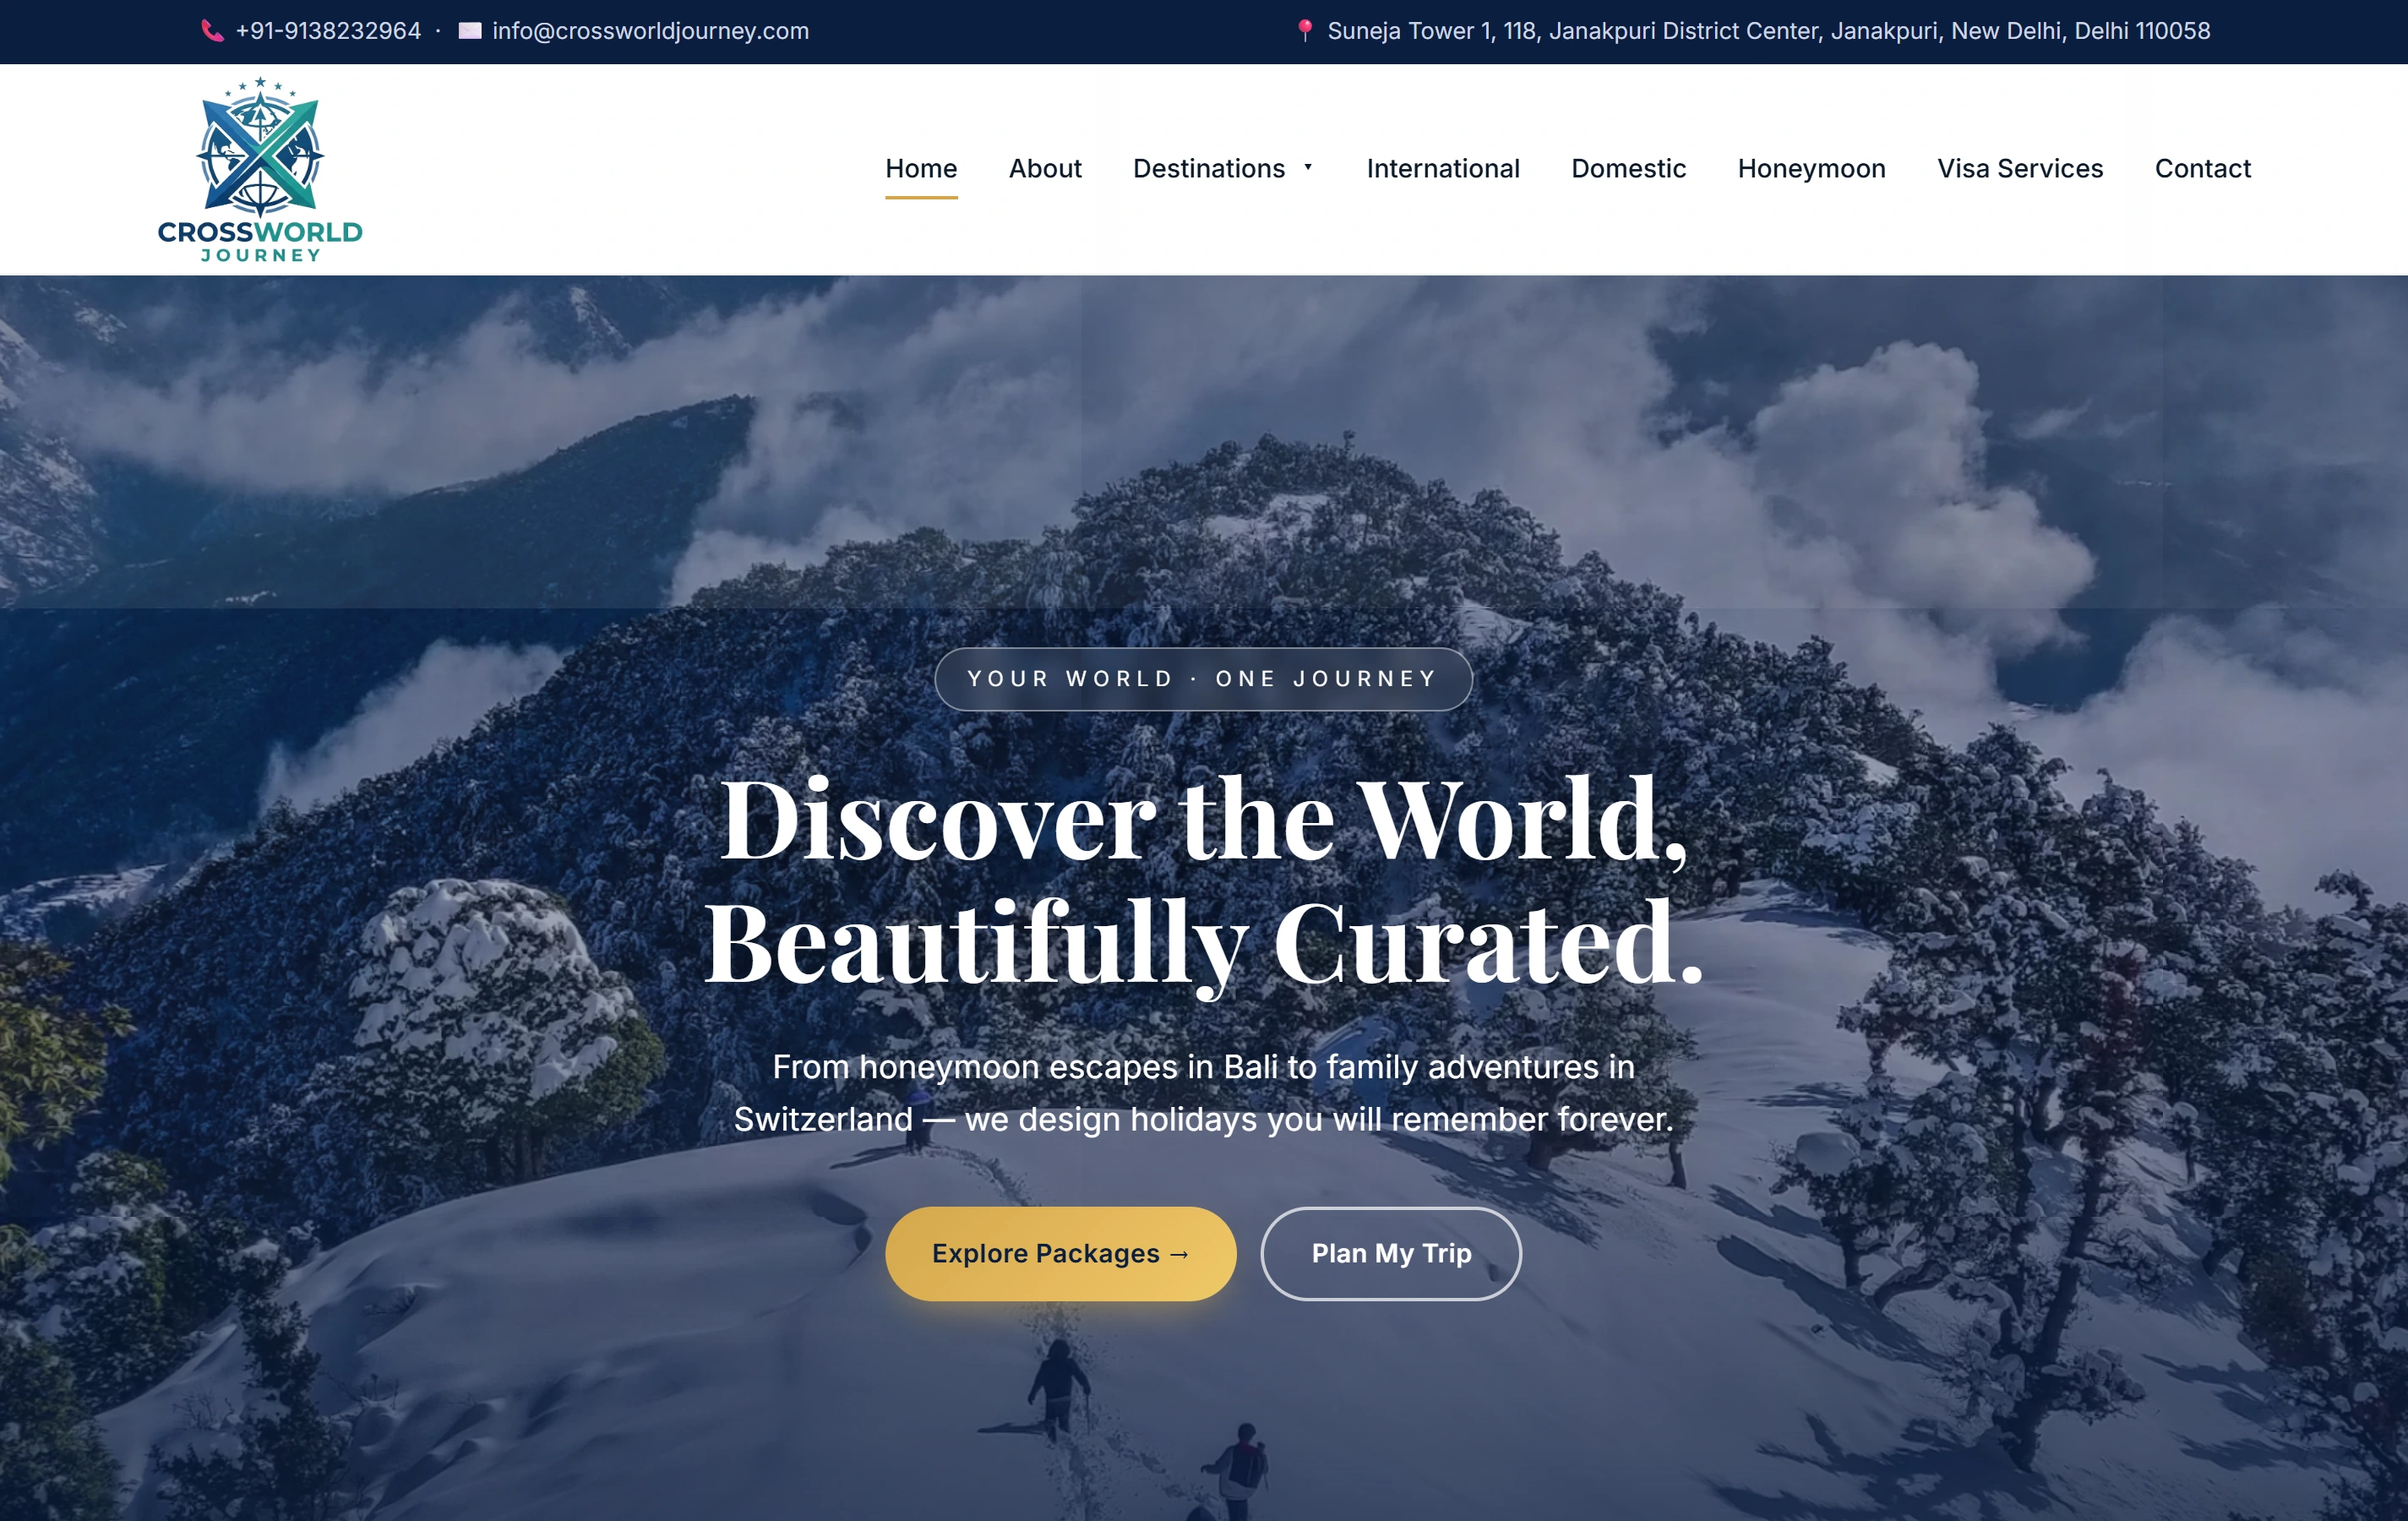
Clear travel information in the Crossworld Journey website.

The Crossworld Journey website organises travel information and gives visitors a route to discuss a trip. It is genuine public website evidence of explaining a service before an enquiry. It does not establish that we delivered a booking backend, a shared-role software system or a project for a New York client. The shared service request on this page is a hypothetical planning example.

Domestic and internationalA broad holiday presentation
Destination informationContext for the trip discussion
Trip enquiryA visible next step
Crossworld Journey websiteCrossworld Journey

Choosing the service and defining the project.

When is custom software justified instead of another subscription tool?

When a meaningful process or integration gap cannot be covered well by a manageable existing product. We compare fit and operating effort in discovery rather than treating custom code as the default.

Can the project use our current applications and records?

We can review documented APIs, exports or approved integration methods and the data to be retained. Feasibility depends on access, permissions and provider limits; migration and connection work must be included explicitly.

Can we deliver one useful workflow before the later modules?

Yes. A first release can focus on the essential users, records and tasks, with acceptance criteria and a later roadmap. Dependencies and operating requirements still need to be reviewed before that release.

How are ownership, cost and post-launch responsibility agreed?

The estimate follows requirements, integration, migration and acceptance effort. The agreement specifies source/data ownership, hosting, licences and external dependencies. Deployment, backups, support and future changes are documented rather than assumed to be included indefinitely.

Can one person be organiser, recipient and payer?

Yes, if that is accurate for the request. Keep the roles explicit even when the person is the same, so a later change of relationship does not require staff to reconstruct who was responsible for each decision.

Does being the payer automatically allow every change?

Do not assume it. Your operating owners must define the permission for each decision. The system should apply the approved rule consistently through both the interface and server-side checks.

Can the first phase avoid automatic customer messages?

Yes. It can end with a reviewed instruction and an assigned internal task. Messages, provider connections and payment processes need separately agreed scope and prerequisites before activation.

How do you deliver work for New York teams?

Softglimmer is based in Ranchi. We can agree remote review sessions and a written handover with your New York operating owners. This page does not claim a New York office, local client or unverified service result.